Security,Compliance&Riskforsoftwarethatneedstrust
Whenthiscapabilityfits
Security, Compliance & Risk is a supporting capability for software projects where trust matters: systems handling personal data, payments, customer accounts, internal business data, regulated workflows, AI outputs, financial processes, KYC, AML, audit trails, or other sensitive operational information. We help build the technical and product foundations that make security and compliance easier to manage — access control, data protection, auditability, infrastructure security, secure workflows, documentation, and risk mapping. This is not standalone legal advice and not a certification service. It is practical technical support for security and compliance decisions, and where formal legal opinions, audits, or certifications are required, we work alongside qualified legal, security, and compliance specialists.
You handle personal or sensitive data
Your system processes customer data, employee data, financial data, health-related information, contracts, or other records that need careful handling. Security and compliance need to be part of how the system is designed, not a checklist item added at the end.
You are building a regulated or compliance-sensitive product
Your product touches finance, payments, investment workflows, digital identity, onboarding, customer verification, or AI-enabled decisions, and needs to hold up against GDPR, NIS2, DORA, ISO 27001, or AI Act expectations. You need help translating those expectations into practical software and infrastructure decisions.
Security was never designed into the system
The data model, permissions, and infrastructure were built without security or compliance in mind, and sensitive information may already be moving through the wrong systems. Fixing this after the fact is slower, more expensive, and riskier than getting it right from the start.
Whatwehelpwith

Security architecture
We design software architecture with security built into the system structure: authentication, authorization, role-based access control, permission models, secure API design, environment separation, secrets management, and logging.
GDPR and data protection readiness
We help design systems that handle personal data responsibly: data mapping, data flow documentation, data minimization, consent and retention logic, deletion and export workflows, and secure storage.
KYC and AML workflow design
A product and technical design engagement for onboarding, identity verification, document collection, review, escalation, and audit workflows, often connected to third-party identity or compliance providers.
NIS2 and cybersecurity readiness
Support for the technical and operational controls behind cybersecurity obligations: risk mapping, access control, incident visibility, logging and monitoring, backup and recovery, vulnerability management, and infrastructure hardening.
ISO 27001 readiness support
We support the technical and operational foundations that help companies prepare for ISO 27001-related work: asset mapping, access control review, infrastructure review, documentation support, and technical evidence preparation.

AI Act and AI risk readiness
We help teams design AI-enabled products and workflows with appropriate controls: use case risk assessment, permission-aware AI access, human-in-the-loop review, audit logs, provider selection, and fallback behavior.
Security architecture
We design software architecture with security built into the system structure: authentication, authorization, role-based access control, permission models, secure API design, environment separation, secrets management, and logging.
GDPR and data protection readiness
We help design systems that handle personal data responsibly: data mapping, data flow documentation, data minimization, consent and retention logic, deletion and export workflows, and secure storage.
KYC and AML workflow design
A product and technical design engagement for onboarding, identity verification, document collection, review, escalation, and audit workflows, often connected to third-party identity or compliance providers.
NIS2 and cybersecurity readiness
Support for the technical and operational controls behind cybersecurity obligations: risk mapping, access control, incident visibility, logging and monitoring, backup and recovery, vulnerability management, and infrastructure hardening.
ISO 27001 readiness support
We support the technical and operational foundations that help companies prepare for ISO 27001-related work: asset mapping, access control review, infrastructure review, documentation support, and technical evidence preparation.
AI Act and AI risk readiness
We help teams design AI-enabled products and workflows with appropriate controls: use case risk assessment, permission-aware AI access, human-in-the-loop review, audit logs, provider selection, and fallback behavior.
Howweworkin4steps
Discovery
We start by understanding what the software does, who uses it, what data it handles, and what happens if something goes wrong. Security should reflect actual risk, not a generic checklist.
Mapping and architecture review
We map data, users, responsibilities, and third parties, then review the architecture, access model, APIs, infrastructure, and operational controls behind it. This is where most hidden risks become visible.
Priorities and controls
We prioritize gaps by data sensitivity, business impact, and regulatory relevance, then turn risk into concrete decisions: permissions, logging, safer workflows, and secure infrastructure.
Implementation and maintainability
We implement the technical changes directly, support your team, or coordinate with legal, compliance, and audit partners, then design controls that stay maintainable as the system evolves.
Ourclients
Selectedprojects
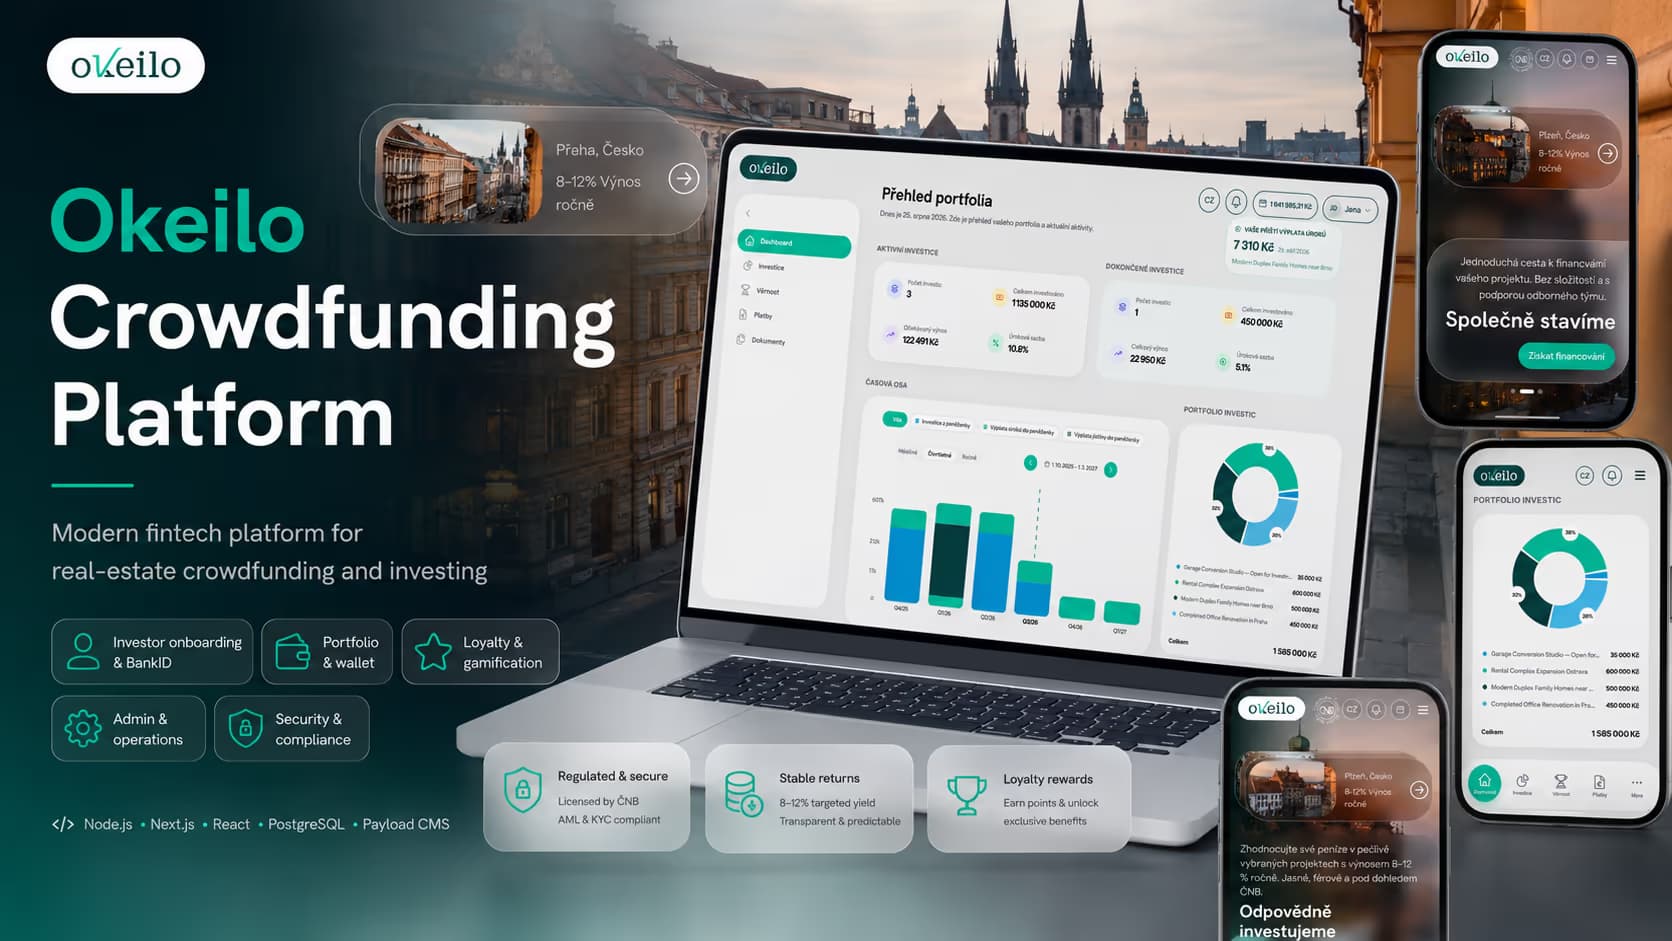
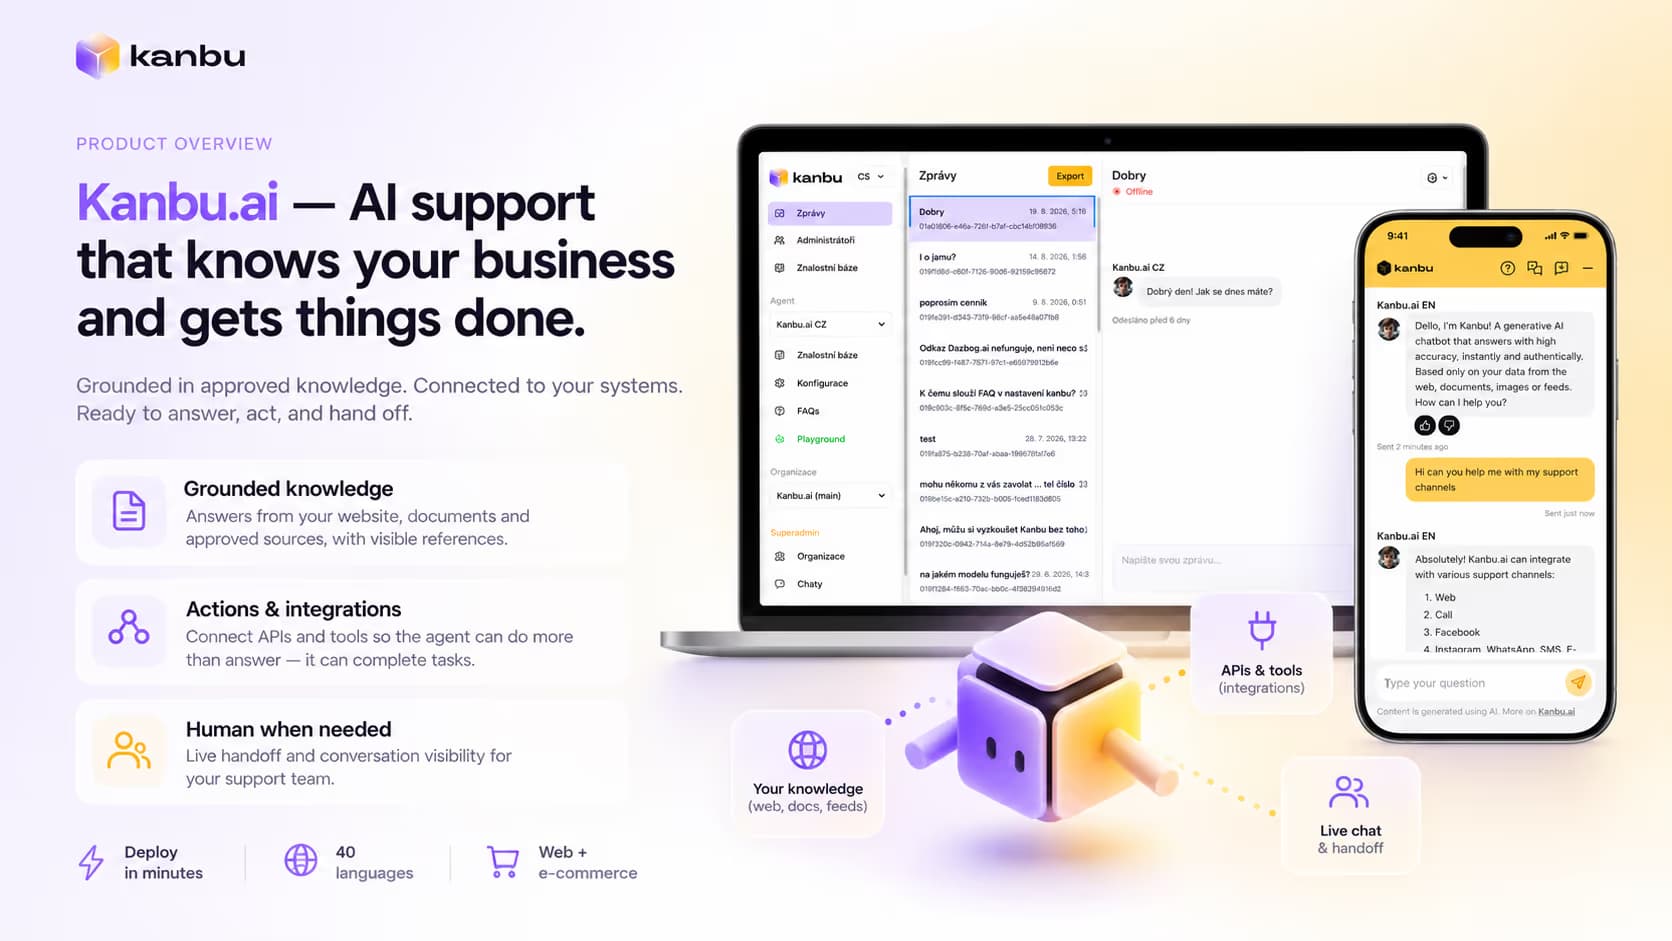
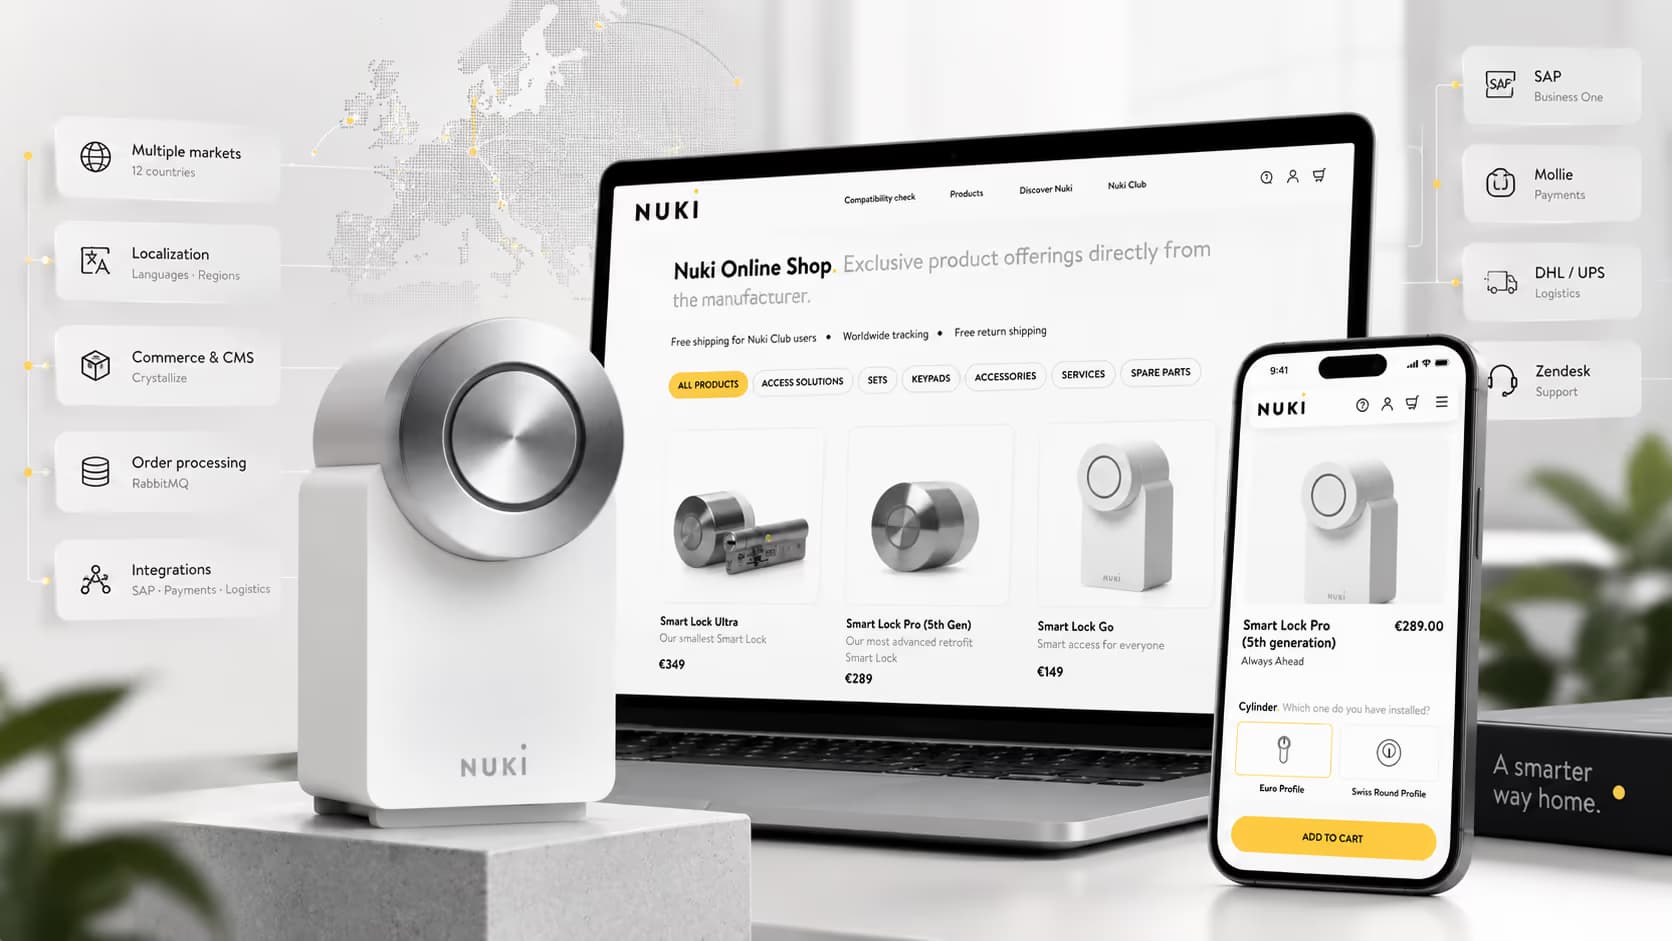
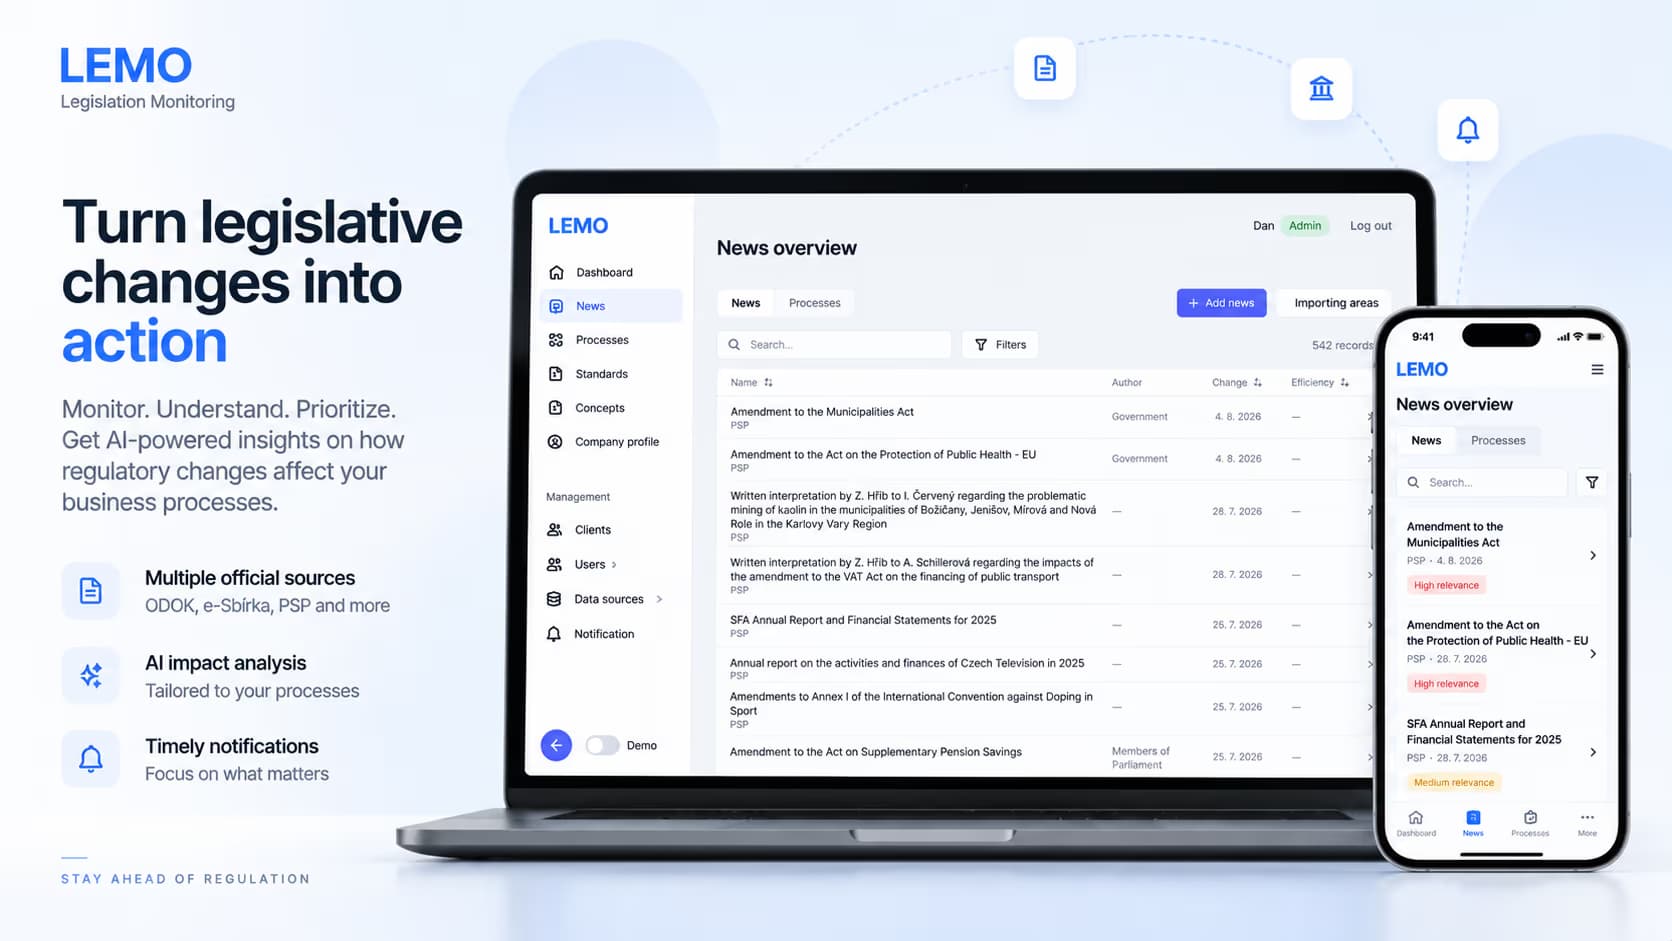
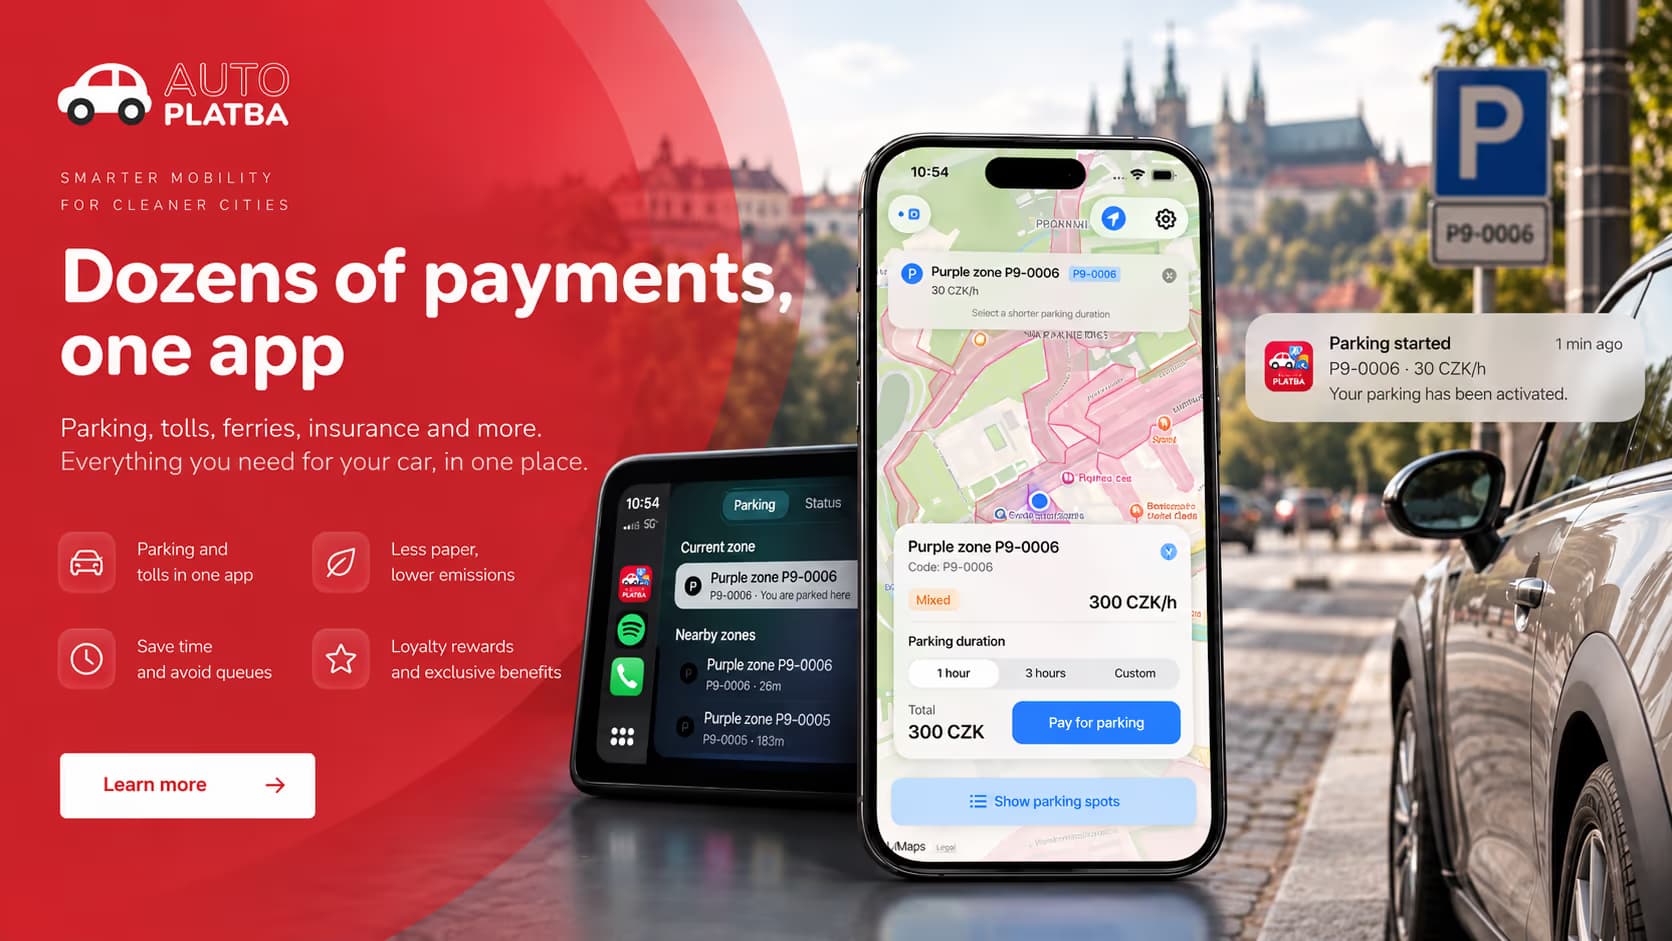
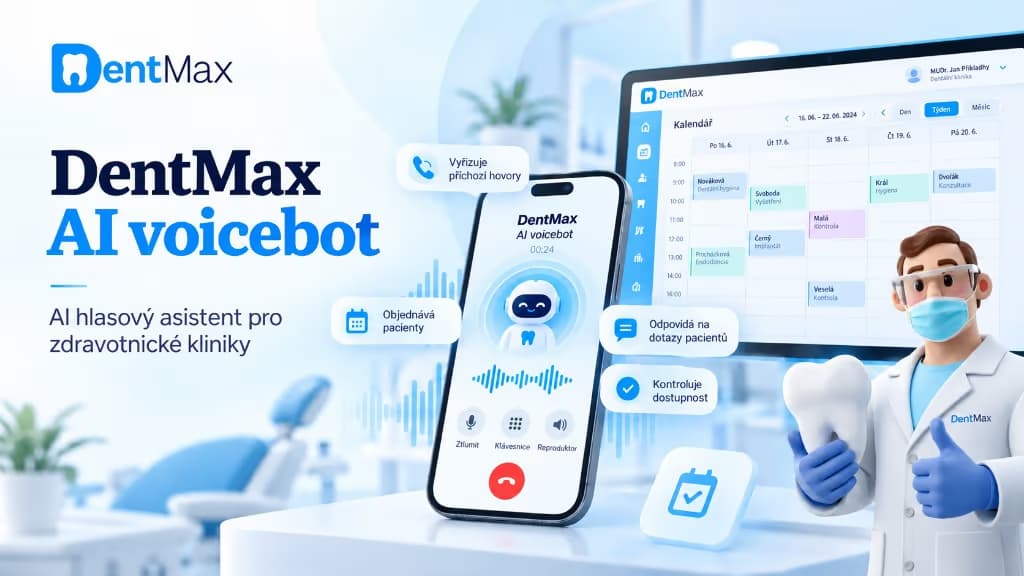
From regulated FinTech and RegTech platforms to AI systems, marketplaces, and large e-commerce ecosystems.
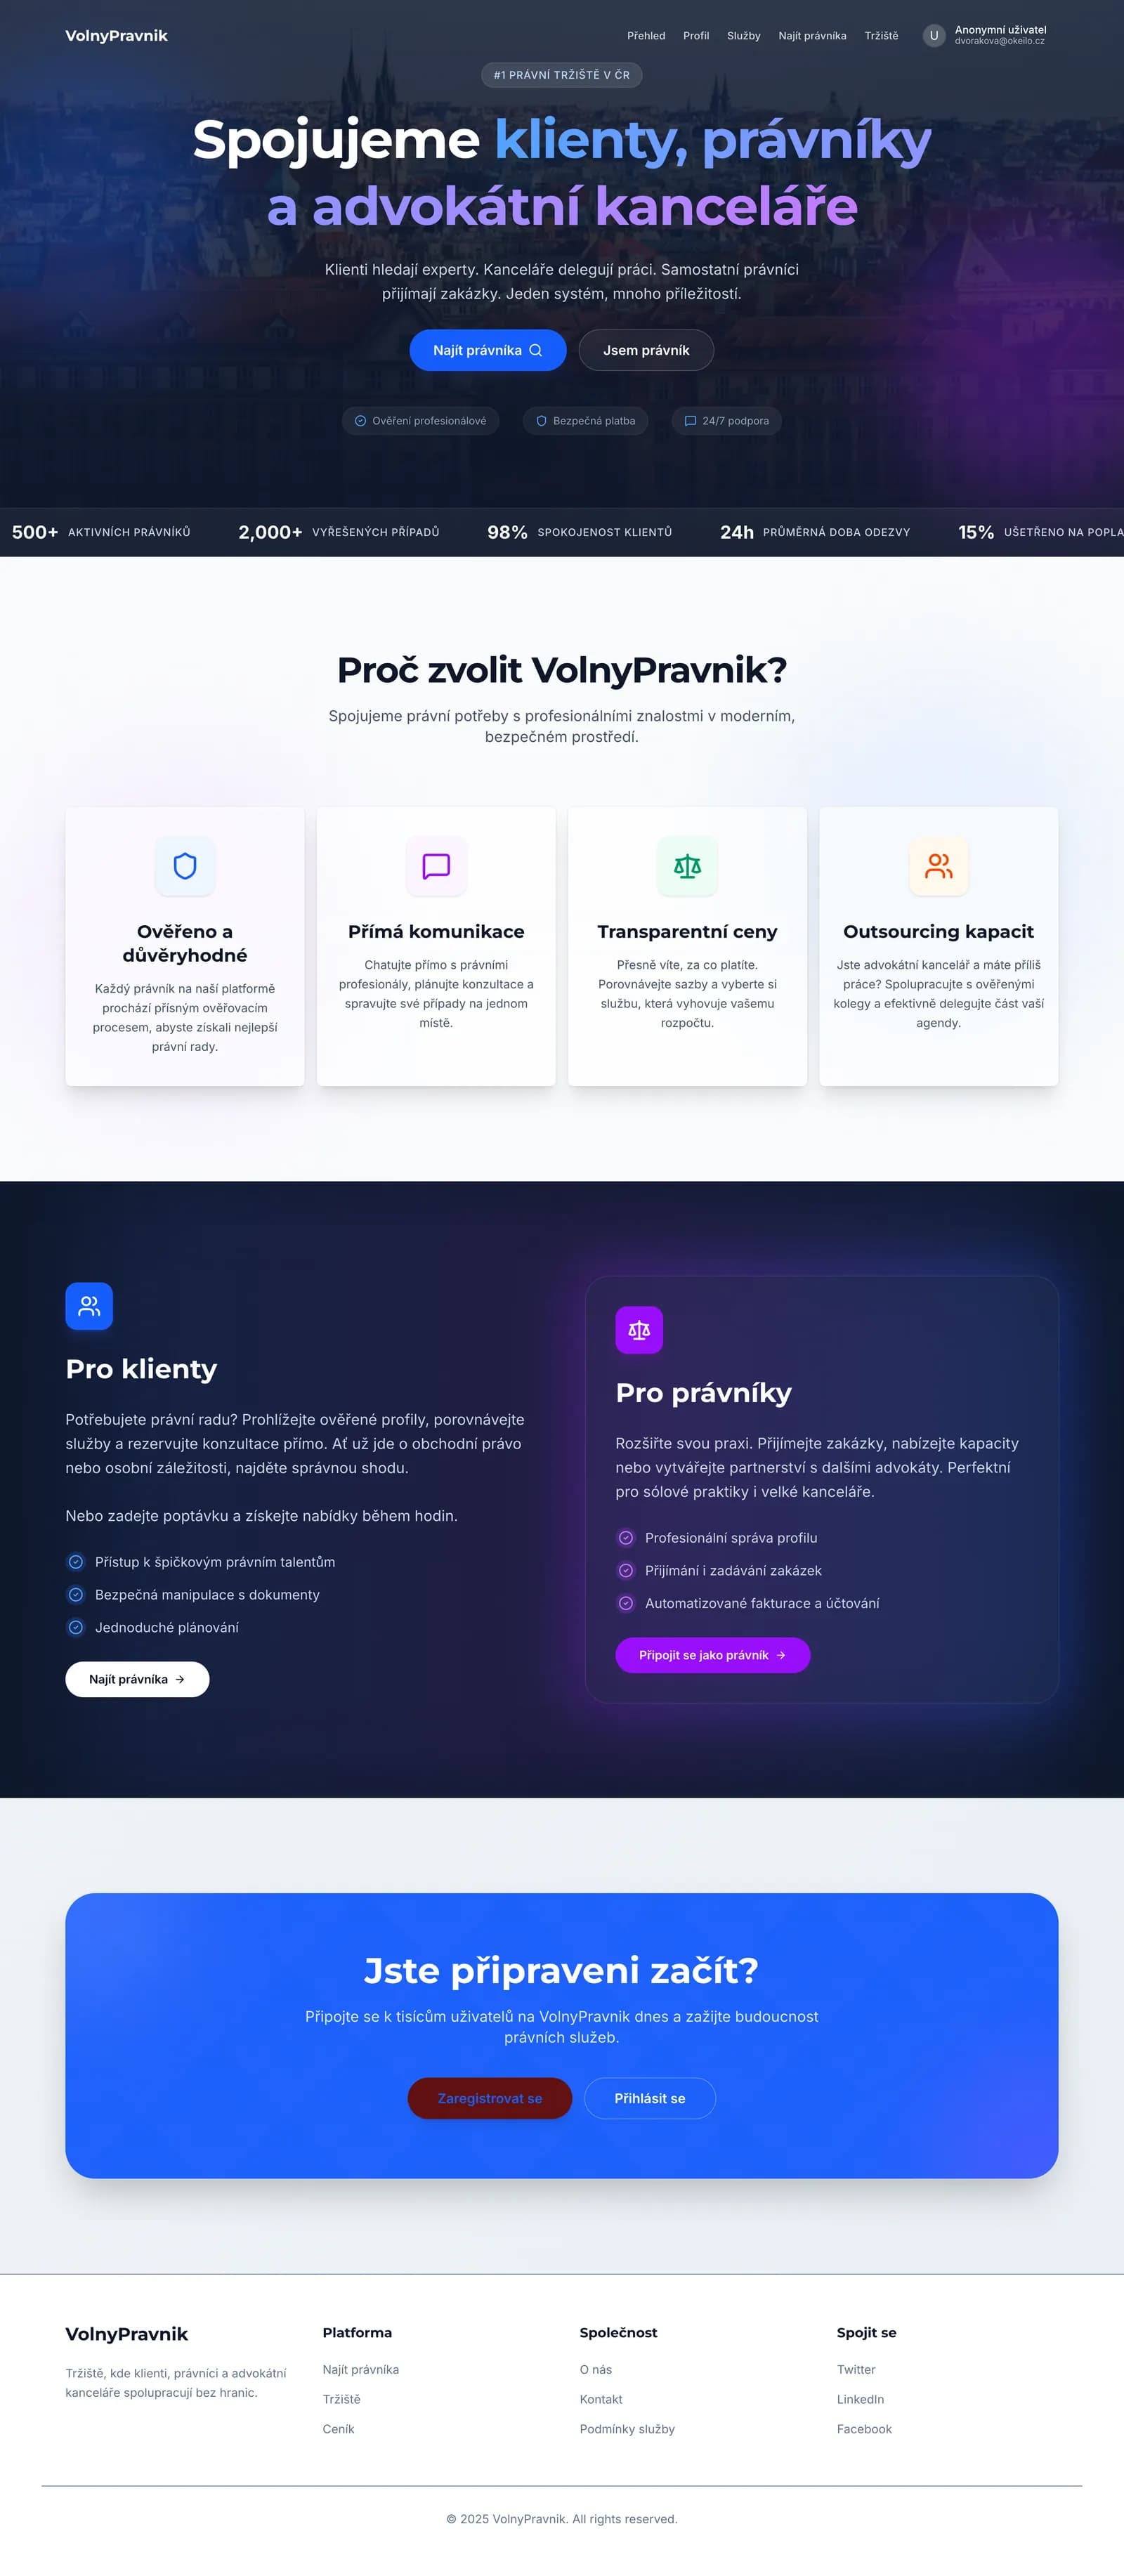
Lawyers Marketplace
Website and marketplace platform for attorneys and law firms
WhyDevehopeforSecurity,Compliance&Risk

We connect compliance to implementation
Compliance requirements do not only live in documents. They affect product flows, data models, infrastructure, permissions, and operational processes. We help turn those requirements into real software decisions, and we design controls that work in production, not only on paper.

We keep AI risk practical
AI creates useful new capabilities, but it also changes the risk profile of software. We focus on practical controls: source grounding, permissions, human review, logging, monitoring, provider choice, and fallback behavior.

We work alongside legal and compliance specialists
We do not pretend that technical implementation replaces legal responsibility. Where formal interpretation, certification, or audit is needed, we support the technical side and work with the right specialists, in the context of your wider architecture, DevOps, AI, and data work.